Blog
March 6, 2025

AI Center of Excellence
The DataPivot AI Center of Excellence brings together AI governance, cybersecurity, data protection, and risk management—so you can discover your AI environment, reduce exposure, establish guardrails, and enable responsible innovation.
Shadow AI Discovery | Governance & Guardrails | Secure AI Adoption at Scale
Employees are using generative AI tools. Business units are evaluating platforms. Technology teams are connecting AI to internal applications and data. Vendors are embedding AI into products you already own.
In most organizations, that adoption is moving faster than governance, security, and risk programs can respond. The AI Center of Excellence provides the structure needed to answer the hard questions—and turn AI risk into a manageable business program.
We help you move forward deliberately: discover what’s in use, decide what’s acceptable, protect what matters, and scale the use cases that earn their place.
Engagements can start anywhere—most begin with discovery, because you cannot govern what you cannot see.
Most AI risk traces back to data access. These are the questions we help clients answer — and keep answering as the environment changes.
Six phases that take you from unknown AI usage to a governed, measurable capability the business can build on.
Identify AI applications, use cases, data flows, vendors, integrations, and the stakeholders behind them.
Evaluate current capabilities, identify control gaps, classify risks, and determine organizational maturity.
Establish policies, decision rights, ownership, intake processes, and oversight structures.
Implement guardrails across identities, data, applications, models, devices, APIs, agents, and connectors.
Embed AI governance into business processes, technology operations, procurement, security, and enterprise risk.
Measure effectiveness, monitor change, test controls, and adapt as AI capabilities and risks evolve.
Targeted engagements that plug into the program—or stand on their own.
Evaluate how AI vendors collect, process, retain, secure, and use your organization’s data.
Prepare for sensitive-data disclosure, unauthorized AI usage, compromised models, malicious prompts, unsafe agent behavior, and AI-enabled fraud.
Help people use AI safely and responsibly — tailored to the audience rather than delivered one-size-fits-all.
Design secure architectures for enterprise AI platforms, private AI environments, generative applications, agents, RAG, and connections to internal data.
Depending on the engagement, deliverables may include:
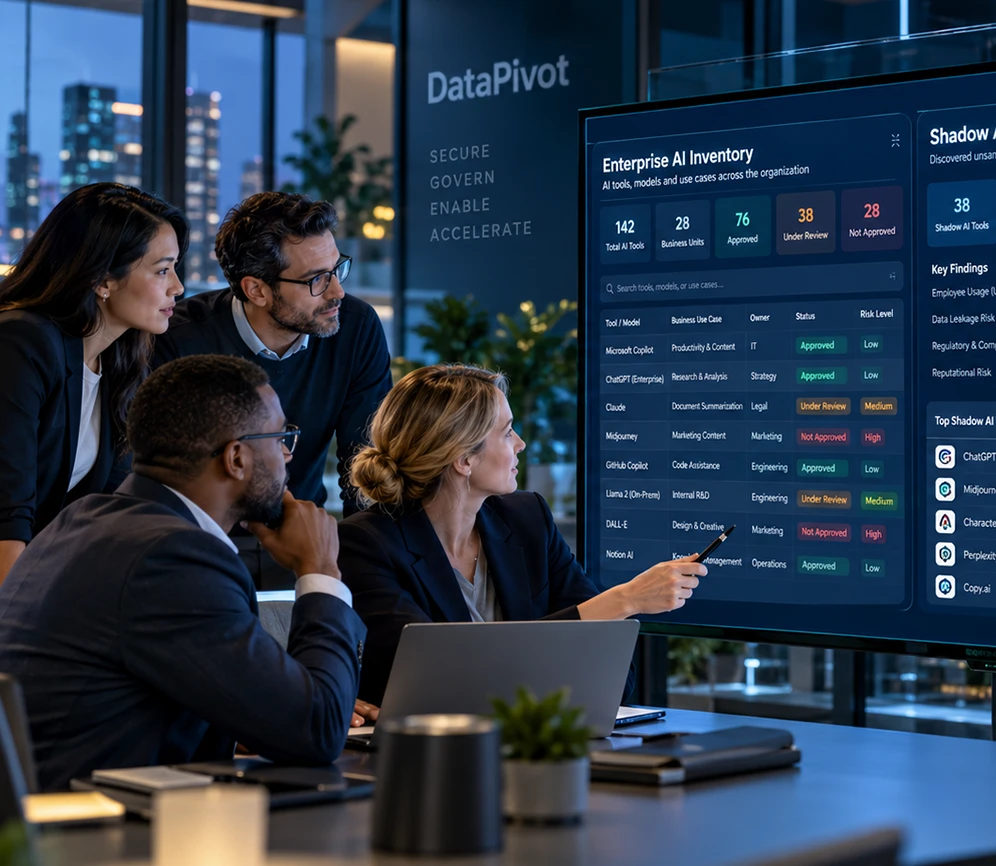
AI success depends on more than picking the right model or application. It depends on confidence in the data, identities, applications, devices, integrations, and controls surrounding it. That is the layer DataPivot has always worked in.
Whether you are beginning your AI journey, responding to rapid employee adoption, or preparing to scale enterprise AI, the AI Center of Excellence provides the governance, security, and operating model to move forward responsibly.


Understand where AI is being used, identify your highest-priority risks, and establish a practical roadmap for secure and responsible adoption.